Container Image Signing and Verification in CI Pipelines
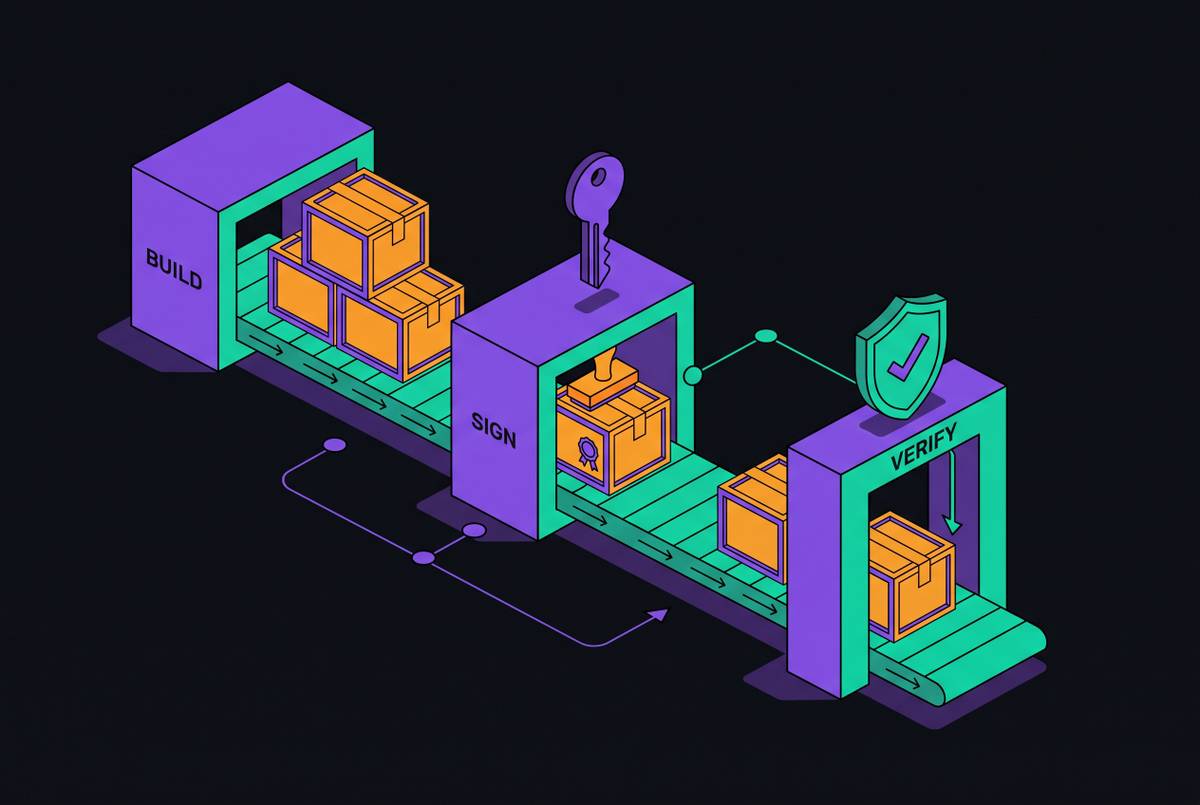
Cryptographic proof that container images came from trusted builds and haven't been tampered with.
Amara Osei-Bonsu
Contributing Editor
Amara is a former security architect who spent eight years advising fintech firms on compliance frameworks before joining Cloud Infra Weekly as a contributing editor in 2021. Her coverage focuses on the intersection of cloud-native security posture and regulatory obligation, with a particular eye toward zero-trust network design.
3 stories
Cryptographic proof that container images came from trusted builds and haven't been tampered with.
Running Kubernetes-based CI/CD saves money and lets you customize infrastructure to your needs.
Three cache layers—dependency, artifact, and remote—each prevent different monorepo CI failures.